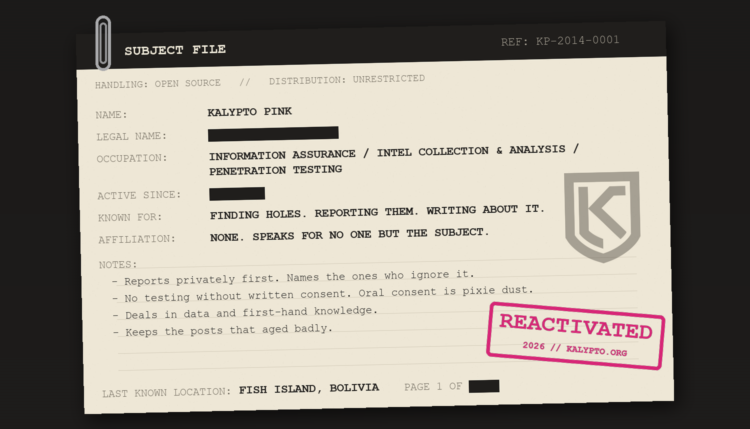
My name is Morgan. The name I have done research under since the Kalypto.net days is “Kalypto Pink”, and it is the name companies, journalists, and a few governments have known me by when I told them something was broken.
I work in information assurance, intelligence collection and analysis, and penetration testing. I have done that work for private companies, for people who needed help, and for governments, across a hacking career that started long before it became a professional one.
What I do here
This site is where I publish what I find and what I think about it. Since 2014 that has included:
- Vulnerability disclosures. Holes I found, reported, and (usually) watched get fixed. Alienware Arena, Smith & Wesson, Cyberoptix, Chili’s Ziosk tablets, Buffalo Wild Wings, Facebook, Arris and NetGear hardware, a Russian regional government, and others. A partial list of organizations is on the Who I Helped page. Some asked me not to name them. I honor that, and I also remember which ones ignored the report until it cost them.
- Research. Large-scale looks at what is sitting exposed on the internet. In 2017 that was fifteen thousand open MongoDB servers in the United States, nearly all of them ransomed within ten days of my first scan. It has also covered source control leaks, reverse proxy exposure, dynamic data masking in SQL Server, and password manager misuse.
- Tools. Things I built for the research and released so others could use them: MRIT (MongoDB Ransom Investigation Tool), TRAFFICCAM, and Windows 10 Privacy Advocate, all on GitHub.
- Analysis and opinion. Leaks and the people behind them, election security, net neutrality, who controls access to information and what they do with it. I used to keep that separate from the technical work. I stopped pretending the two are separable.
Everything from 2014 through 2019 is still here, including the posts that aged badly. I don’t delete my record.
How I work
- I report what I find to the people who can fix it, before I write about it, and I give them a reasonable window to do so.
- I write from data and first-hand knowledge. If I am speculating, I say so. If I don’t know, I say that too.
- I don’t test what I don’t have written consent to test, and I tell other researchers to do the same. Oral consent is pixie dust.
- Opinions here are mine alone. They do not represent any employer, client, or organization I have ever been associated with.
If I contacted you about a vulnerability
You are not being extorted, and I am not selling anything. I found a problem in something you run, I am telling you so you can fix it, and I would like to be able to write about the issue and the fix afterward, because a lesson nobody can read is not much of a lesson. If you need the details redacted or the company unnamed, ask. If you ignore the report, that becomes part of the story.