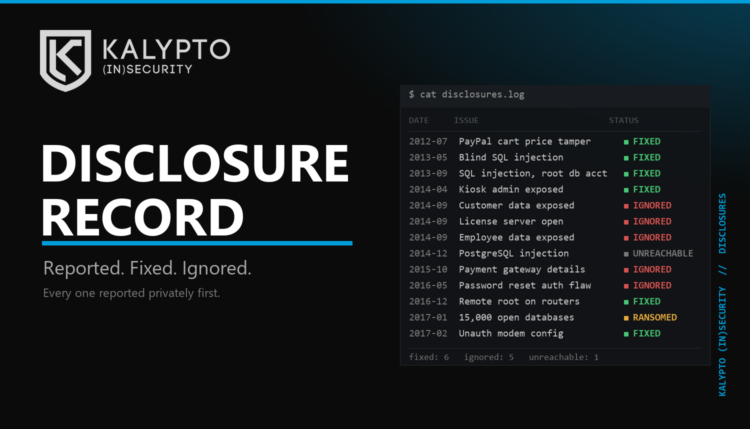
This is a record of security problems I have found and reported over the years, and how the people responsible handled it. It is not complete. Most organizations asked not to be named, and I honor that. Some findings are still unpatched, so the details stay vague until they are fixed.
Every one of these was reported privately before anything was published. The “Response” column is the part I care about most. Fixing a hole is expected. How a company treats the person who told them about it says more about their security than any policy page.
Reported and fixed
| Organization | Issue | Reported | Response |
|---|---|---|---|
| Alienware Arena (Dell) | Blind SQL injection, database not locked down | 2013 | Fixed. Courteous throughout, and they sent a thank-you. |
| Smith & Wesson | SQL injection via ad redirect; database account had full root | Sept 2013 | Silence for six weeks, then a quick patch once they understood it. Fixed Dec 2013. |
| Brinker (Chili’s) and Ziosk | Table-top kiosk configuration and admin access reachable by patrons; same hardware at Applebee’s | April 2014 | Ziosk responded within a day and fixed it. Exactly how it should go. |
| NetGear | Remote root command execution on far more router models than initially reported | Dec 2016 | Updated their advisory to the full model list and shipped firmware. |
| Cyberoptix Tie Lab | PayPal cart accepted any price the buyer sent, including zero | July 2012 | Grateful. Small shop without the means for a code fix, so they now approve every order by hand. They sent me a tie. |
| Arris | Cable modem configuration changes with no authentication, triggered by visiting a web page | Feb 2017 | Engineering reached out within days. Patched within six weeks. |
Reported and ignored
| Organization | Issue | Reported | Response |
|---|---|---|---|
| Mobile password reset handed over the wrong account with no challenge | May 2016 | Dismissed through their White Hat program. Others found and demonstrated it publicly a month later. | |
| Buffalo Wild Wings | Kiosk and Wi-Fi exposure with enough detail to reach the payment gateway | Oct 2015 | Two contact attempts, Twitter, Facebook, and a conversation with a manager. Nothing. Still unfixed when I stopped checking. |
| Radixx International | Unsecured access to customer data and internal information | Sept 2014 | No response to two reports. |
| BIOMIDS | Unsecured licensing server; intellectual property exposure | Sept 2014 | No response to two reports. |
| IntravNews | Unauthenticated web service could generate valid license keys | Sept 2014 | No reply. The site went offline instead. |
| A U.S. defense contractor (unnamed) | Employee IDs, schedules, and personal details exposed | Sept 2014 | “We will be working to secure our site.” Still open a month later. Unnamed because of what they build. |
| Tambov regional government, Russia | PostgreSQL injection on the public site | Dec 2014 | Every email bounced and every contact form timed out. I tried. |
Also reported
Findings I have not written up, or that were handled entirely in private: CJ Pony Parts, Maricopa Community College, Microsoft, Sig Sauer, Springfield Armory, and others.
And roughly fifteen thousand MongoDB operators in the United States whose databases I found open in January 2017, most of which were ransomed before anyone could be told. That one gets its own post.
If you are on this list
If your entry is out of date because you fixed the problem, tell me and I will update it. Gladly. If you would like to be moved off the ignored list, the way to do that is to respond.
To the companies I help going forward: please let me write about the issue and the fix once it is closed. A lesson nobody can read teaches nobody anything.